 Coffermap · Data briefs & subscriptions
See where federal dollars land
See where federal money lands in your county, ranked, in one Excel file.
Checkout by Polar
from $15▶ Open the spending mapView
Store › Data briefs & subscriptions › Kevscope Brief

Patch what's being exploited first. A 12-page data brief built from CISA's Known Exploited Vulnerabilities catalogue (version 2026.09.23), FIRST's EPSS scores (2026-09-23) and every CVE NVD published from 25 August to 24 September 2026.
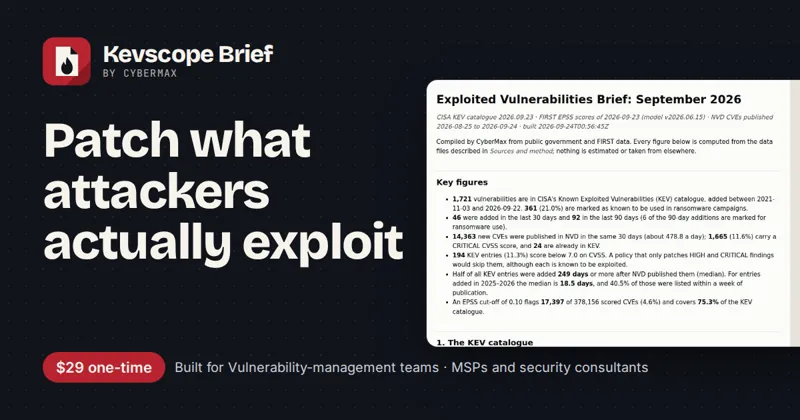
| CVE | Vendor | Product | CVSS | EPSS | KEV due |
|---|---|---|---|---|---|
| CVE-2026-94127 | F5 | BIG-IP APM | 9.3 CRITICAL | 1.39% | 2026-09-25 |
| CVE-2026-85102 | Check Point | Multiple Products | 9.8 CRITICAL | 0.66% | 2026-09-25 |
| CVE-2026-93952 | Arista | VeloCloud Orchestrator | 9.5 CRITICAL | 0.74% | 2026-09-25 |
| CVE-2026-93616 | Check Point | Multiple Products | 9.8 CRITICAL | 2.42% | 2026-09-25 |
| CVE-2026-7273 | Zyxel | GS1900 Series Switches | 8.8 HIGH | 2.41% | 2026-09-24 |
appendix: KEV additions 25 Aug–22 Sep 2026 (CISA KEV 2026.09.23, EPSS 23 Sep)
Patch what's being exploited first. A 12-page data brief built from CISA's Known Exploited Vulnerabilities catalogue (version 2026.09.23), FIRST's EPSS scores (2026-09-23) and…
Buy nowPatch what's being exploited first. A 12-page data brief built from CISA's Known Exploited Vulnerabilities catalogue (version 2026.09.23), FIRST's EPSS scores (2026-09-23) and every CVE NVD published from 25 August to 24 September 2026.
Inside
You get the PDF, an HTML version, three CSV tables (KEV additions, upcoming deadlines, critical watchlist) and the Python script that computes every number from the public data, so you can check it or rerun it. Every figure comes from the data; nothing is estimated.
Who it's for: security and IT teams deciding what to patch this month, MSPs writing client updates, and analysts who need sourced numbers for a report.
Information only; not a substitute for your own vulnerability management. Not affiliated with CISA, FIRST or NIST.
Licence: use inside your organisation and quote figures with attribution; don't resell the brief as-is. One-time purchase, instant download. © 2026 CyberMax.
Checkout is handled by Polar. Your download, licence key or API key and your receipt arrive by email right after payment.
Yes. If it doesn't work as described, email us within 14 days and we fix it or refund you in full. See the refund policy.
Card details go only to Polar (merchant of record, payments by Stripe). CyberMax never sees them; sales tax or VAT is calculated at checkout.
Kevscope Brief · from $15
Coffermap · Data briefs & subscriptions
See where federal money lands in your county, ranked, in one Excel file.
 Curvewire Brief · Data briefs & subscriptions
Every Monday: the US yield curve, rates and macro numbers on one page.
 Kevscope Weekly · Data briefs & subscriptions
Know what attackers exploited this week, every Monday.
 Bonafido API · APIs & MCP
Is this company website real? One call checks a domain, URL or email: DNS, domain age, mail setup, the live homepage, parked or for-sale…
Prices and plans generated from live Polar data on 27 Sep 2026.